Recent research by Claroty has exposed a critical blind spot in global data center security: nearly one in five operational assets is just a single network hop away from a potential cyberattack. Analyzing over 750,000 cyber-physical systems, the findings paint a stark picture of the vulnerabilities lurking within power distribution, cooling, and building management systems (BMS).
While enterprise IT networks are heavily fortified, the operational technology (OT) that keeps the lights on and servers cool often relies on legacy architectures. As data centers scale rapidly to support the AI boom and global cloud infrastructure, this massive disparity between IT and OT security is creating a ticking time bomb for facility uptime.
The ‘One Hop’ Illusion and Lateral Movement
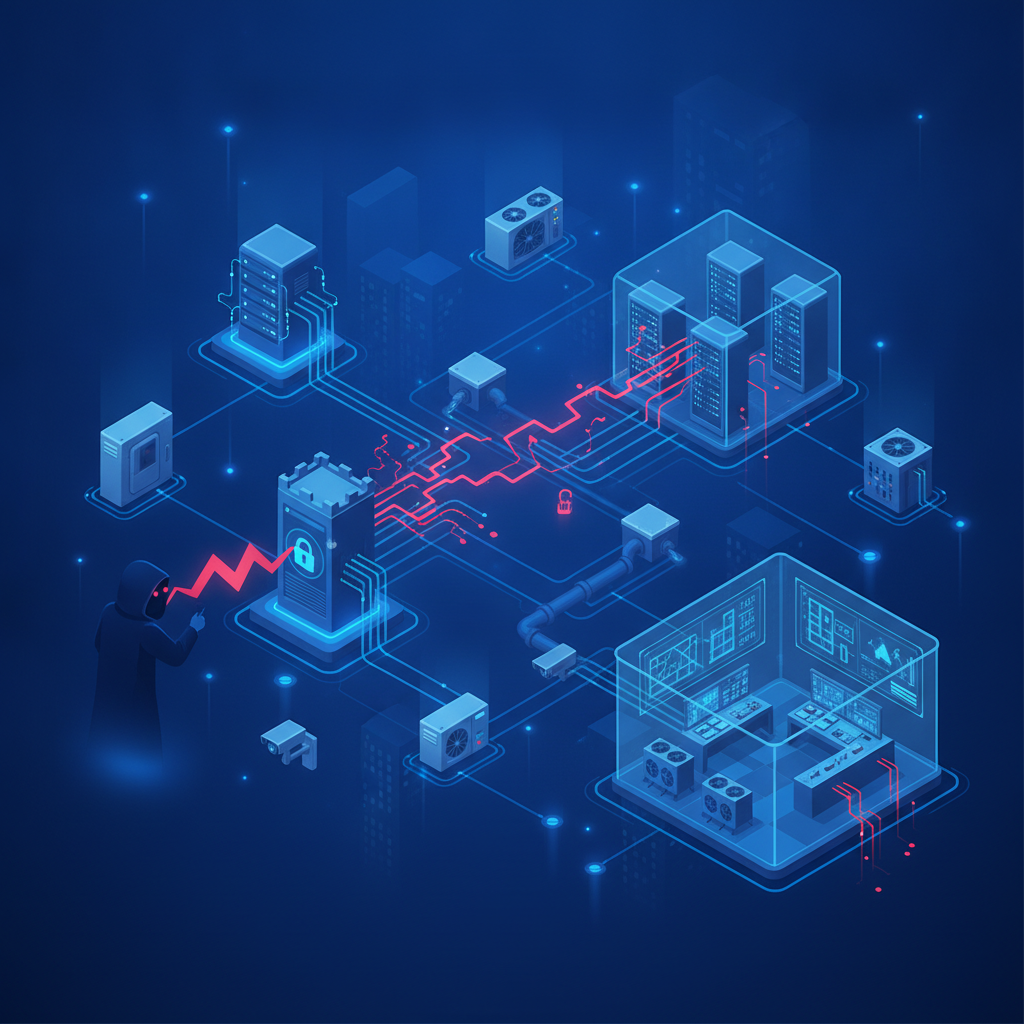
Many facility managers operate under the dangerous assumption that because their HVAC systems or power distribution units (PDUs) aren’t directly connected to the public internet, they are secure. However, the Claroty report completely shatters this illusion, highlighting the extreme danger of network lateral movement.
If a threat actor breaches a seemingly innocuous, internet-connected IoT device in the lobby, they are often just one network step—or “hop”—away from critical infrastructure. In fact, an alarming 41% of PDUs and 32% of cooling systems fall into this highly exposed category.
Once inside, attackers don’t even need to breach heavily encrypted server racks to cause chaos. Simply manipulating chiller setpoints or tripping electrical breakers via an exposed BMS can trigger cascading thermal failures, bringing multi-million-dollar AI workloads to an abrupt halt.
Legacy Protocols in a Modern Threat Landscape
A staggering 88% of building management systems analyzed in the study communicate over insecure protocols, and over 80% of OT control systems rely on legacy standards like BACnet and MODBUS.
As a building automation architect, I frequently see how these protocols—which were engineered for reliability and open interoperability—lack the native encryption and zero-trust authentication required today. Without aggressive network segmentation, they remain highly susceptible to packet sniffing and command spoofing if the perimeter is breached.
Compounding the issue is the fact that 40% of these systems run on outdated firmware. Facility operators are often paralyzed by the fear of operational downtime, choosing to leave critical patches unapplied rather than risk a controller reboot. Consequently, nearly a quarter of connected IoT devices in data centers contain publicly known, actively exploited vulnerabilities.
Bridging the Dangerous IT/OT Divide
The fundamental root cause of these ICS security failures is the historic divide between IT cybersecurity teams and facility operations. Building systems are frequently managed by third-party contractors or siloed engineering teams with entirely different priorities than the Chief Information Security Officer.
With data centers now underpinning critical global infrastructure—from financial networks to logistics and public services—this divide is an unacceptable business risk. Uptime is the currency of the data center industry; an operational disruption affecting cooling is virtually indistinguishable from a ransomware attack in its impact on customer SLAs and institutional trust.
Securing the Core with Modern Building Automation
Protecting these complex ecosystems requires a shift from isolated, perimeter-based defense to active exposure management, strict network segmentation, and continuous telemetry. Facilities must modernize their BMS infrastructure and limit internal pathways without compromising the underlying continuity of operations.
This is exactly where modern cloud-managed ecosystems like BAaaS.io provide a critical advantage. By centralizing control and unifying property-wide infrastructure onto a secure, authenticated network, operators can eliminate the blind spots associated with fragmented legacy building automation systems.
BAaaS.io features robust role-based access controls, continuous real-time telemetry, and automated environmental monitoring. It actively bridges the IT/OT gap by bringing enterprise-grade cybersecurity and proactive maintenance to legacy BACnet environments, effectively shutting down the lateral movement pathways that hackers exploit.
Conclusion
Data centers have evolved into the critical infrastructure of the modern digital economy, making their operational resilience an urgent priority for both economic and national security. Treating power, cooling, and automation controls as secondary to data security is a massive risk that operators can no longer afford.
By acknowledging the deep-seated vulnerabilities in legacy protocols and embracing unified, secure building management platforms, facility operators can finally close the “one hop” gap. True data center resilience requires securing the physical operational environment just as fiercely as the servers housed within it.