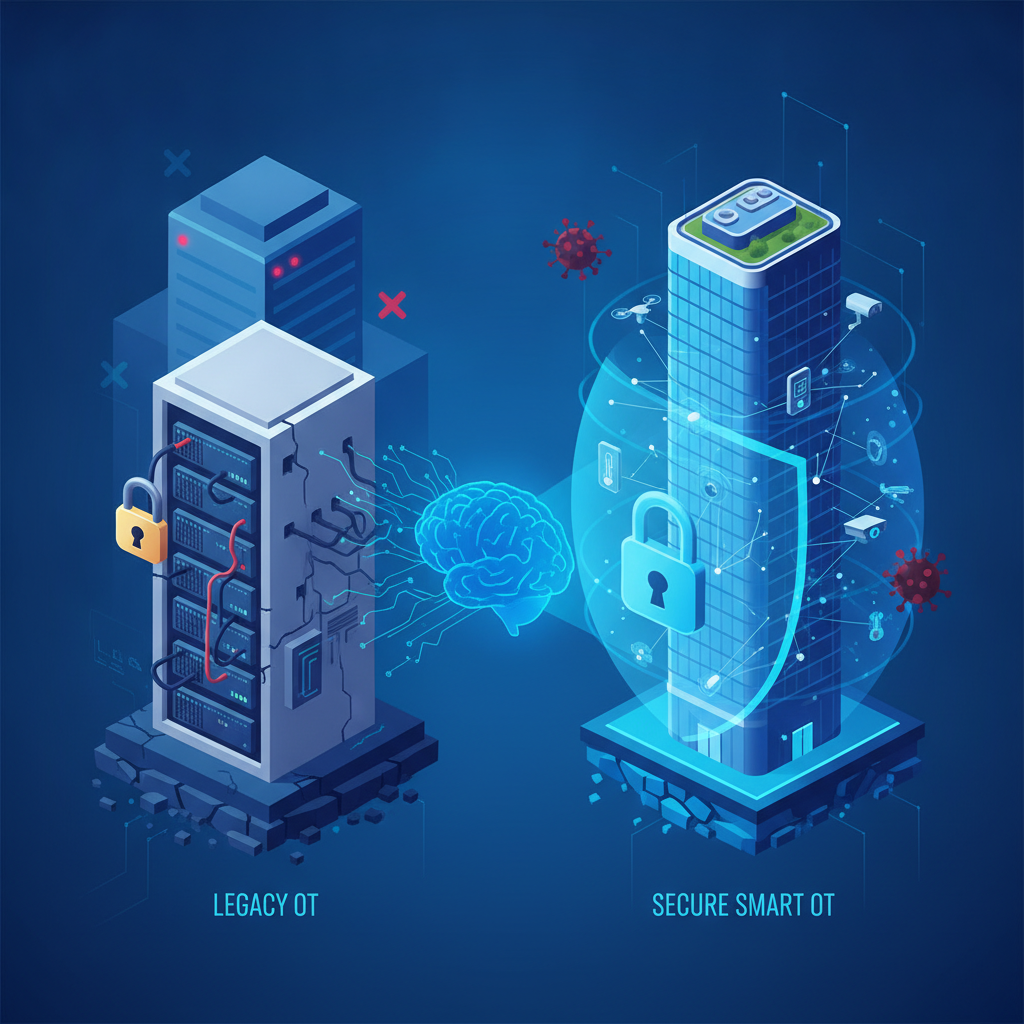
The building automation industry has long operated under a false sense of security. While confirmed cyberattacks on smart building systems are statistically rare, this rarity masks a critical vulnerability in how we architect Operational Technology (OT) and Internet of Things (IoT) networks.
For decades, facility managers have expected Building Management Systems (BMS) to natively defend these environments. However, as threat landscapes evolve, it has become increasingly clear that relying solely on a BMS to own both operational control and cybersecurity is a dangerous architectural flaw.
The BACnet Security Paradox
For sixteen years, the BACnet protocol included a dedicated security clause that remained largely unimplemented. In 2019, ASHRAE made the practical decision to delete it entirely. This was not because the underlying cryptography was fundamentally flawed, but due to a staggering lack of industry uptake.
This historical footnote perfectly illustrates the core problem with smart building cybersecurity. Security cannot simply be bolted onto legacy communication protocols. When building operators expect traditional BMS platforms to natively secure complex OT environments, they are leaning on features that the industry historically ignores, finds too complex to manage, or fails to deploy effectively.
When Rarity Becomes Reality: The KNX Exploit
The persistent argument that “buildings don’t get hacked” was recently put to the test. In July 2026, CISA added CVE-2023-4346—a critical defect in the KNX protocol’s Connection Authorization Option 1—to its Known Exploited Vulnerabilities catalog. A core building automation protocol was actively being weaponized in the wild.
This is highly unusual for the ICS sector. The industry standard, much like CISA’s earlier advisory on Johnson Controls iSTAR controllers, usually ends with a comforting caveat: “No known public exploitation specifically targeting these vulnerabilities has been reported.” However, the active exploitation of KNX proves that threat actors are beginning to target the inherent weaknesses of building networks. The rarity of these events should no longer be mistaken for immunity.
The Fatal Flaw in Control Layer Architecture
When cyber incidents do successfully breach connected building systems, they almost always trace back to a single architectural failure: an over-reliance on a flat network where the BMS acts as both operator and primary defender.
The stakes in the physical world are incredibly high. Unlike enterprise IT systems, a compromised OT control layer often cannot be simply restored from a cloud backup. If threat actors overwrite proprietary controller logic, alter HVAC parameters, or lock out lighting systems, the resulting downtime and life-safety risks demand immediate, costly physical intervention rather than just a software reset.
Shifting the Defense Strategy with Cloud Architecture
To truly secure a smart building, facilities must decouple their operational control from their primary security perimeter. This is where a specialized ecosystem like BAaaS.io transforms building operations. By abstracting the control layer into a centralized, secure cloud environment, BAaaS (Building Automation as a Service) provides a unified network to monitor and manage property-wide infrastructure safely.
Instead of relying on outdated protocol-level security that goes unimplemented, BAaaS.io introduces robust access control, built-in authentication, and role-based permissions out of the box. It creates a highly secure “integrated building information sphere” that processes real-time telemetry from HVAC, lighting, and security systems, ensuring the underlying physical controllers are shielded from direct network threats.
Conclusion
The honest framework for smart building cybersecurity isn’t about the sheer volume of attacks—it is about the catastrophic impact of a single architectural failure. As protocols like KNX face active exploitation and legacy BACnet security measures fade into history, the industry must stop relying on the BMS to do it all.
Modern building automation requires a modern, defense-in-depth approach. By leveraging secure, centralized platforms that prioritize robust authentication and proactive monitoring, property owners can protect their most critical physical assets while delivering optimized, intelligent environments for their tenants.